

Admin Playbook for Two Role Digital Signage User Permissions
The safest default for most organizations is a two-role split: Creator handles design and edits, Publisher/Approver reviews and pushes content live, and every role gets scoped to specific screens, groups, or locations rather than the whole account. Layer in SSO and 2FA plus audit logs, and you get fewer broadcast errors, clear accountability when something does go wrong, and the confidence to delegate without hovering over every screen. Some digital signage platforms build this exact model into their platform.
TL;DR:
Most organizations should implement a two-role model with scoped permissions and multi-factor authentication to reduce errors and improve accountability.
Object-level permissions and custom roles help manage access to individual screens, playlists, or locations, especially in larger, multi-location networks.
A content approval workflow that includes at least Creator and Publisher roles, with optional reviewers, prevents outdated or incorrect content from going live.
Proper permission setup involves inventorying screens, creating minimal roles, gradually expanding access, and testing from the lowest privilege levels before going live.
Full audit logs, staged rollouts, and clear documentation are essential for accountability, troubleshooting, and smooth permissions configuration.
Table of Contents
How Do You Set Digital Signage User Permissions by Role?
Most signage networks run on five roles, and each one should map to a specific job, not a specific person’s seniority.
Owner: full account control, billing, and the ability to add or remove admins. Usually one or two people.
Administrator: manages users, screens, and settings account-wide but doesn’t necessarily create content.
Publisher/Approver: reviews submitted content and pushes it live. This is the gatekeeper role.
Creator/Editor: builds and schedules content but can’t publish without approval.
Viewer: sees dashboards, analytics, or playlists with no edit rights.
Scoping matters as much as the role itself. A role capability matrix from a signage vendor typically shows Owner and Admin at the account level, while Creator and Publisher get scoped to a group, location, or player set. A franchise marketing director might need Publisher rights across all 40 locations, while a single store manager only needs Creator access to their own screens. IT operations usually sits at the Administrator level, handling player health and network settings without touching daily content decisions.
RBAC, Custom Roles, and Object-Level Permissions: How Do They Interact?
Role-based access control (RBAC) assigns permissions to a role, then assigns users to that role. It works fine for small teams, but once you cross a few dozen users or multiple locations, the standard five roles start feeling too blunt. That’s when custom roles earn their keep, letting you create something like “Regional Publisher” that can approve content for a set of stores but can’t touch billing or add new users.
Object-level permissions go a step further. Instead of granting access to a whole category, they let you grant or deny actions on a specific playlist, screen, or player. According to BrightSign’s documentation on object permissions, user-specific allows take priority over role-level permissions, which take priority over system defaults. That hierarchy matters when you’re troubleshooting why someone can’t perform an action their role should allow.
Start with the broadest system-level defaults (usually deny-by-default).
Layer role-level permissions on top for standard job functions.
Apply object-level overrides only for exceptions, like a contractor who needs temporary access to one screen.
Pro Tip: Build every override from the lowest-privilege user upward. Testing top-down hides denies that quietly block legitimate work until someone finally notices in production.
What Does a Good Content Approval Workflow Look Like?
Operational error, not malicious tampering, is the primary risk in digital signage networks. An outdated price or a typo in a promotion stays visible to every customer walking past that screen until someone catches it and fixes it. Your approval workflow exists to catch that before it happens, not after.
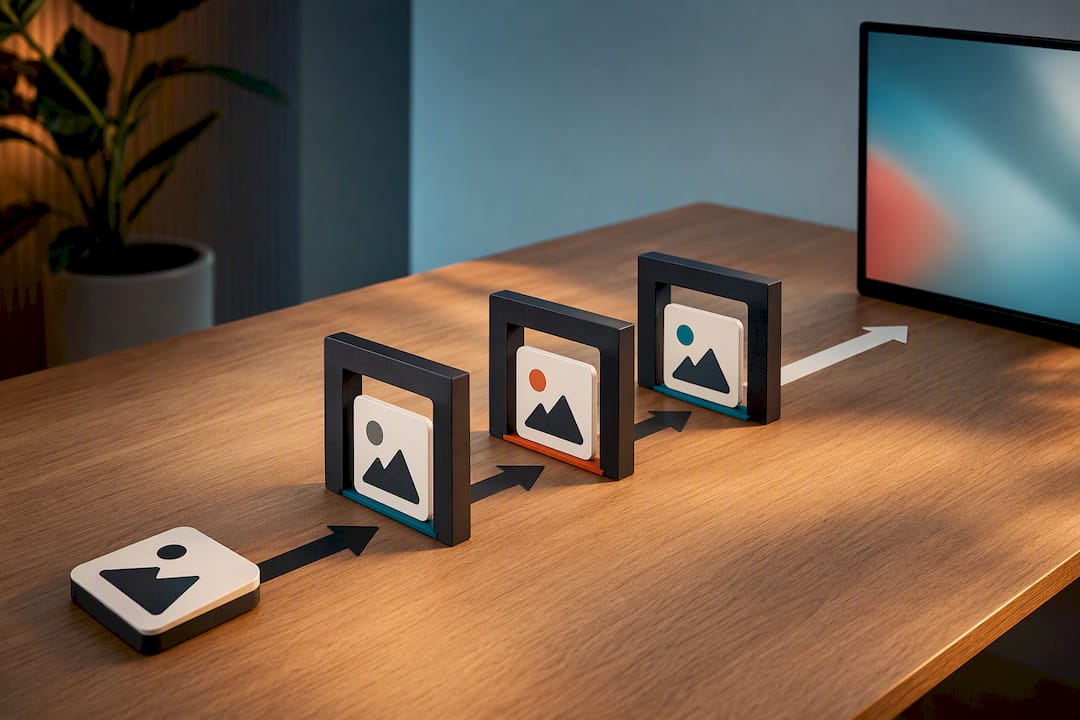
The simplest pattern is Creator submits, Publisher approves and pushes live. A Creator to Publisher gate catches most quality and brand issues on its own. For higher-stakes networks, add a Reviewer step between the two: Creator → Reviewer → Publisher, which spreads accountability across three people instead of two.
Franchise and multi-location networks often need a split ownership model:
Corporate owns brand templates and locked layouts.
Local managers own text swaps, hours, and daily specials within those templates.
A designated approver signs off before anything reaches screens, a pattern some platforms enforce as mandatory design approval.
Preview and hold states are worth enforcing at the platform level, not just as a policy. If publish rights aren’t technically restricted, someone will eventually skip the review step under deadline pressure.
How Do You Roll Out Permissions Without Breaking Anything?
Configuring permissions in the wrong order creates more rework than doing it right the first time. Follow this sequence:
Inventory every screen and assign a named content owner to each one, even if that’s a temporary placeholder.
Create the minimum viable roles first (Creator, Publisher, Admin) and assign least privilege by default; expand only when someone hits a real limitation.
Scope roles by group or location so a regional manager can’t accidentally publish to a store three states away.
Enable SSO and SCIM provisioning along with two-factor authentication. Vendors commonly support these specifically to simplify onboarding and offboarding without manual account cleanup.
Configure mandatory approvers and turn on any setting that blocks publishing without sign off.
Set audit log retention and document the whole workflow in a short runbook so on-call staff aren’t guessing at 11 p.m. on a Saturday.
Pro Tip: Write the runbook before the first incident, not after. A two-page document that says who approves what, and who to call if a screen goes dark, saves more time than any dashboard.
For teams building out that documentation, a content workflow guide can help structure the approval gates so they’re consistent across locations, and a scheduling guide is useful once you start scoping playlists to specific groups.
How Should You Test Your Permission Setup Before Going Live?
Test from the lowest-privilege account upward. Log in as a basic Creator first and confirm they genuinely cannot publish, then move up through Reviewer and Publisher roles to confirm each one can do exactly what it should and nothing more. A sandbox group with two or three dummy screens is worth setting up specifically for this.
Publish access fatigue is the most common failure mode in small-to-midsize networks: too many people get publish rights “just in case,” and any one of them can push an error live. A short list of frequent mistakes to check for:
Conflicting denies where a role-level allow gets silently blocked by an object-level deny.
Missing approvers, meaning content sits in review with nobody assigned to sign off.
Overbroad admin accounts left over from initial setup that never got scoped down.
A staged rollout, automated alerts on publish events, and a scheduled weekly change report catch most of these before they become customer-facing problems.
What Should You Log for Accountability and Investigation?
Every publish action, schedule change, user or role modification, and player reassignment should hit an audit log automatically. Vendor documentation on distribution and communication security recommends retention policies specifically so teams can trace who published what and when, months after the fact.
When something does go wrong, a simple playbook works better than improvising: identify the exact item that broadcast incorrectly, roll it back or remove it immediately, notify whoever owns that location or brand relationship, and record what happened and why.
Weekly digest of publish changes across the network.
Monthly review of who belongs to which role.
Quarterly full permissions audit against your original runbook.
Governance Should Never Slow Down Good Operations
Most organizations overbuild their permission structure before they’ve even launched their first campaign. Two roles, Creator and Publisher, cover the vast majority of use cases, and adding a third or fourth tier before you’ve hit an actual problem just adds approval friction nobody asked for. Expand the model when a specific incident or scaling need demands it, not because a org chart looks incomplete with only two boxes.
The rollout tip that gets skipped most often: change permissions gradually, location by location, rather than flipping the whole network to a new model overnight. That single choice prevents most of the confused support tickets that come with a permissions migration.
— DKS
See SignStream’s Permission Controls in Action
If the model above sounds right for your network but the idea of configuring it manually feels like a project you don’t have time for, that’s exactly the gap SignStream closes with its Automated Publishing Platform. Role-based permissions, mandatory approval gates, SSO and SCIM support, and full audit logs are features offered by some digital signage platforms, often along with scoped groups so a location manager only manages their own screens.
You don’t need a technical background to set any of this up. Creators submit, Publishers approve, and every action gets logged automatically, whether you’re running three screens in one gym or three hundred across a franchise network. See exactly how the permission and scheduling controls work together on the SignStream platform overview, and if monetizing your screens through the ad exchange marketplace is part of your plan, the ad display network page walks through how that layers on top of the same role structure.
Vendor Docs Worth Bookmarking
These sources cover the mechanics referenced throughout this guide in more technical depth:
Mandatory Design Approval docs: a real-world enforced approval gate.
Content approval workflow explainer: the reasoning behind Creator to Publisher gates.
Sources
FAQ
What Are the Main User Roles in Digital Signage Software?
Most platforms offer Owner, Administrator, Publisher/Approver, Creator/Editor, and Viewer roles, each with progressively narrower rights, and each one can typically be scoped to specific screens or locations rather than the entire account.
What Are Common Digital Signage Mistakes Admins Should Avoid?
The most frequent mistakes are granting publish access too broadly, leaving conflicting allow and deny rules unresolved, and skipping a formal approval step, all of which let an incorrect price or promotion reach live screens before anyone catches it.
Are There ADA Requirements for Digital Signage Content?
Yes. Digital signage used in public-facing spaces generally needs to meet accessibility standards for text size, color contrast, and readability, and permission systems should ensure only trained reviewers can approve content before it publishes to confirm it meets those standards.
What Are the Disadvantages of Digital Signage If Permissions Aren’t Managed Well?
Without clear roles and approval gates, networks risk outdated or off-brand content staying live for hours, accidental publishes to the wrong location, and no clear record of who made a change when something breaks.
Does SignStream Support Role-Based Permissions and Approval Workflows?
Yes. SignStream includes role-based permissions, scoped group access, approval workflows, and audit logging so admins can delegate content creation without giving up control over what actually reaches screens.
Recommended
Comments